Your code stays unreadable
Anti reverse-engineering shieldWhat ships is not what was written. Whoever opens the tools is recorded, with who and where.
30-day free trial · 1 app · no cardWatch mode by default: no change for your users
Vaultedo watches every attempt to copy your app: an anti reverse-engineering shield over your code, anti-clone and anti-scraping gates in front of your data, and a forensic watermark on every screen that names who saw it. Real users never notice a thing.
One app, watch mode, no card. Sign in with Google, Microsoft or your email.
The visitor's window, the gate in front of your data and your console. Select a scenario; they also play in turn.
No data: the gate refused this request.
waiting for the first event
Select a scenario above; they also play in turn.
The four ways people copy a web application, played out live: the window, the gate and your console. Press an attack and watch what you would be told.
What ships is not what was written. Whoever opens the tools is recorded, with who and where.
Your pages on any other address get the frame and none of the data, and the copy files itself in your console.
A watched session is served as always. Anything else asking for your data is refused and named.
No page can stop a screenshot. Every screen carries its viewer, so a leaked picture names who took it.
Wherever your application runs. Your users notice nothing while it goes in, and your console shows each step for your platform.
Logos are the trademarks of their owners, shown to say where Vaultedo runs; no affiliation or endorsement is implied.
Vaultedo speaks the Model Context Protocol, so the coding agent your team already uses can add it, deploy it and test it for you.
Logos are the trademarks of their owners, shown to say which tools Vaultedo works with; no affiliation or endorsement is implied.
Every app with its state and its switches; an x-ray of each with charts you can press; alerts, an audit log, your team, the plan. These are the real screens.
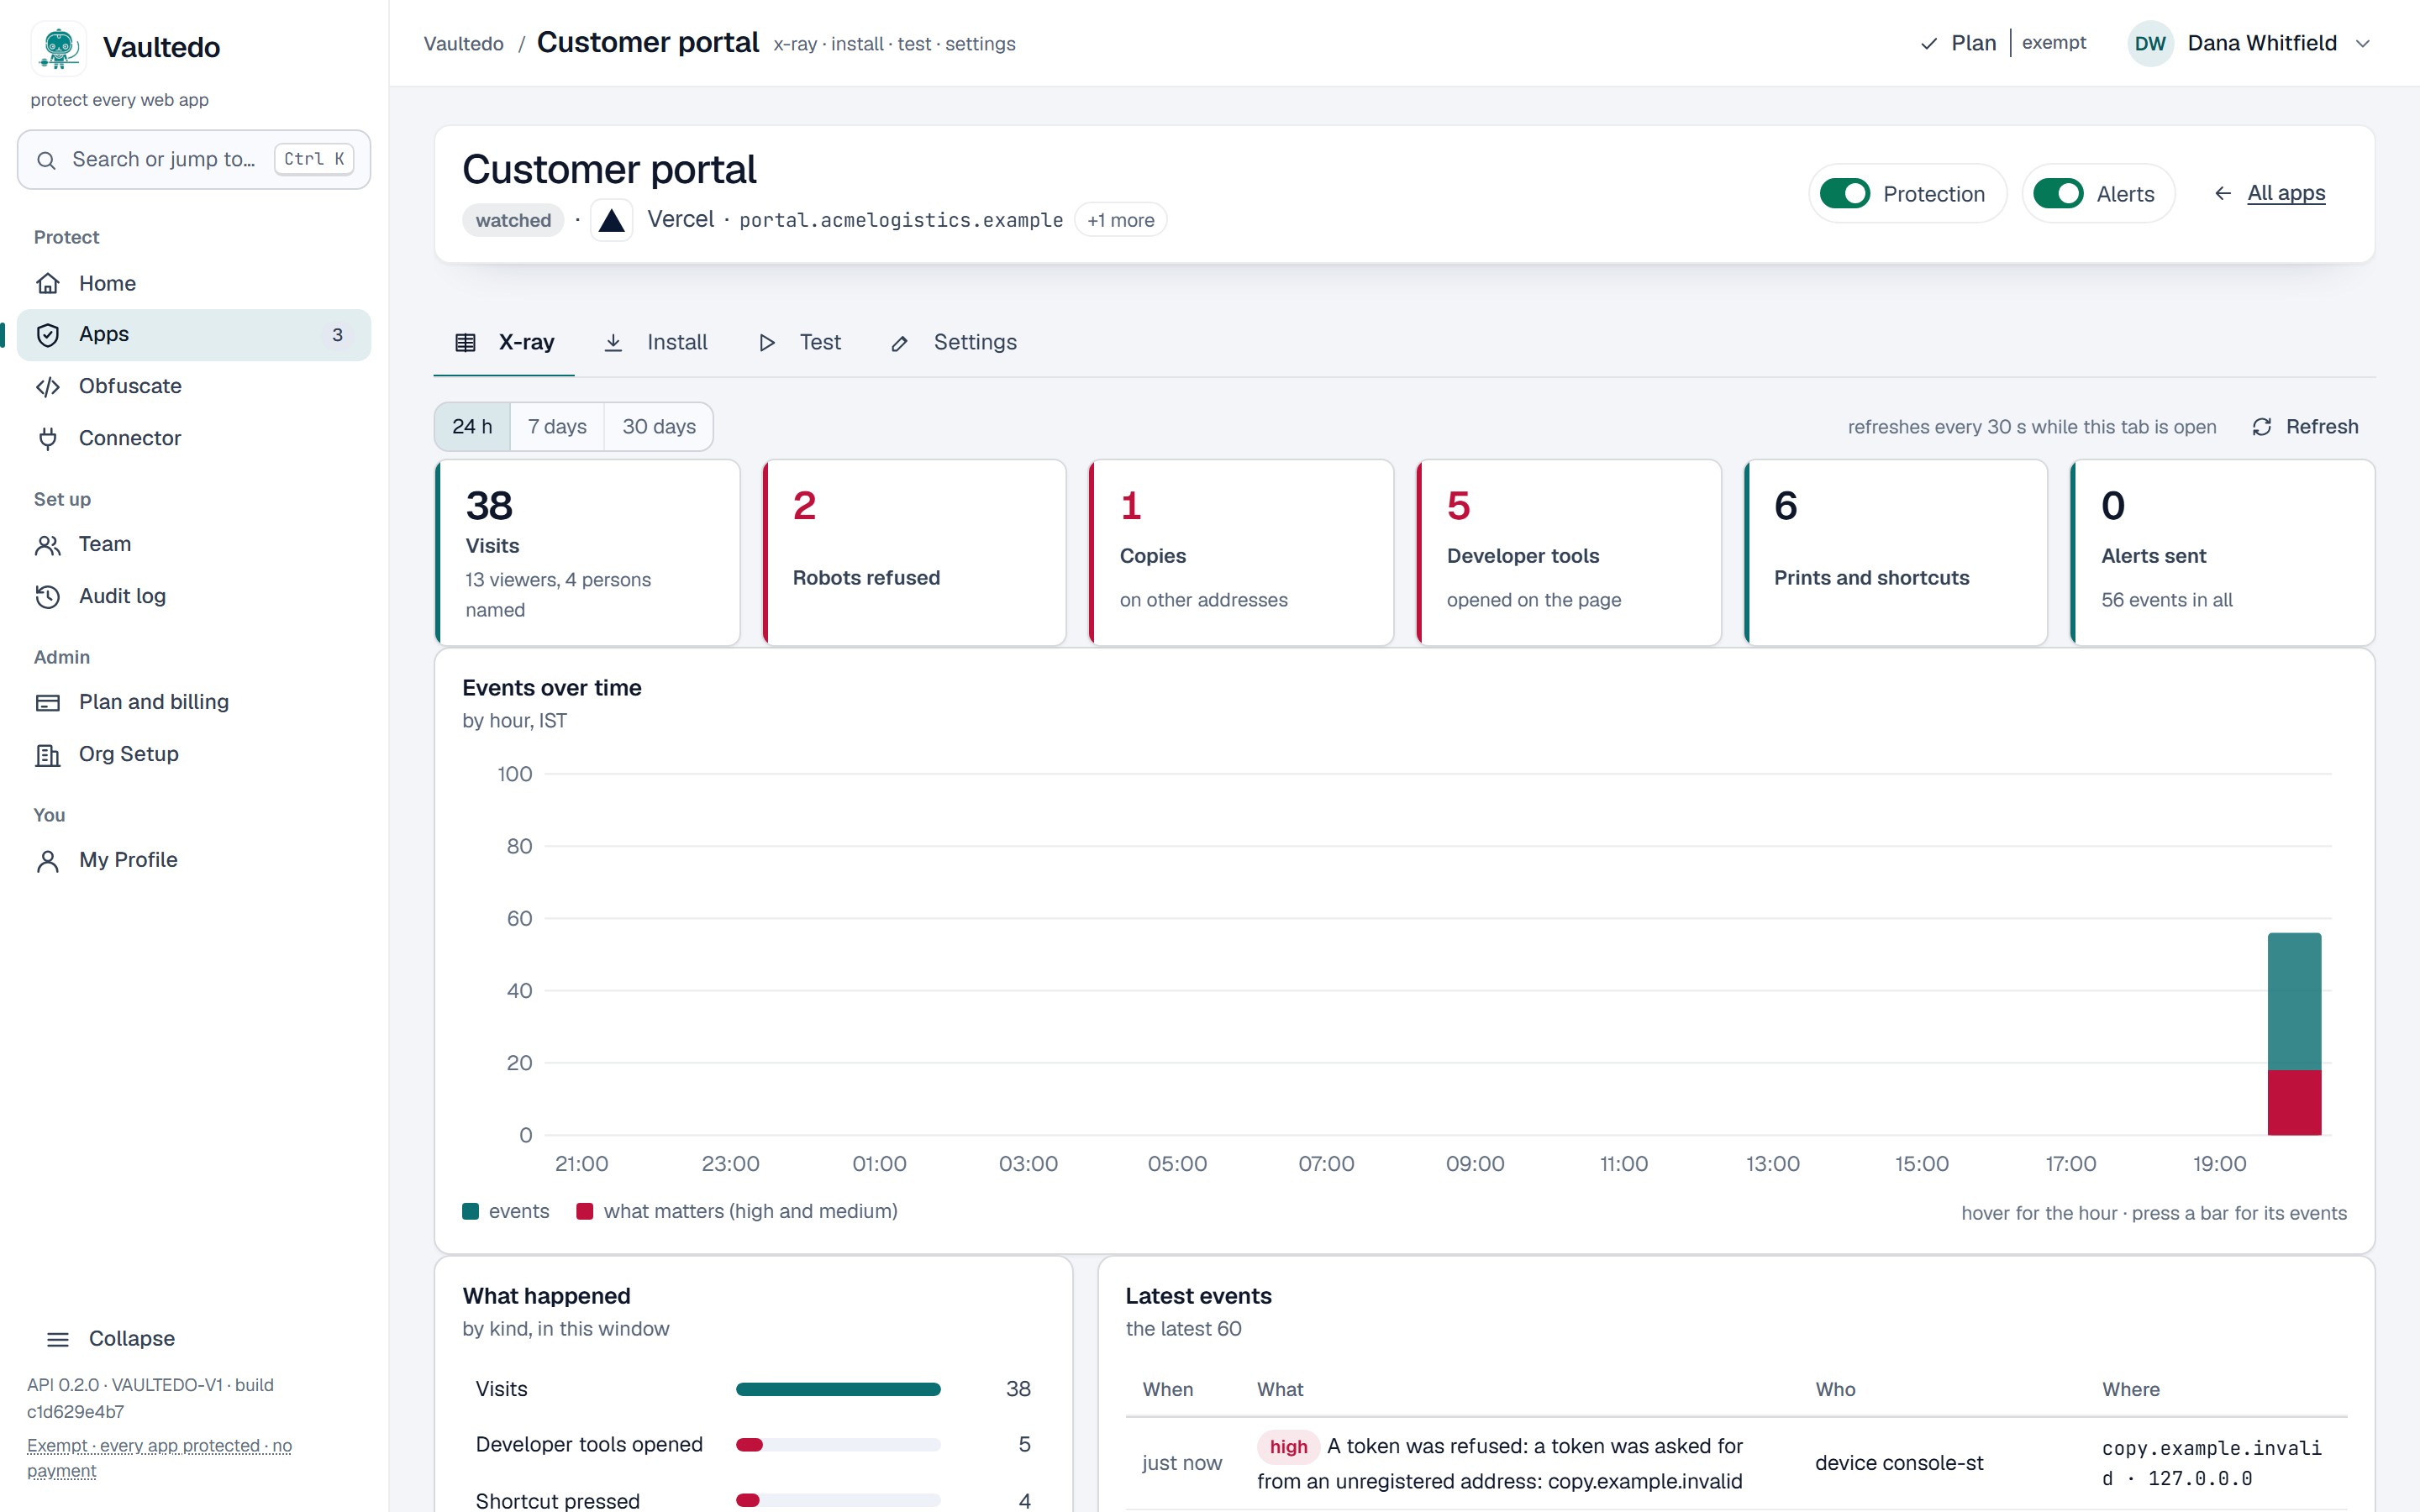
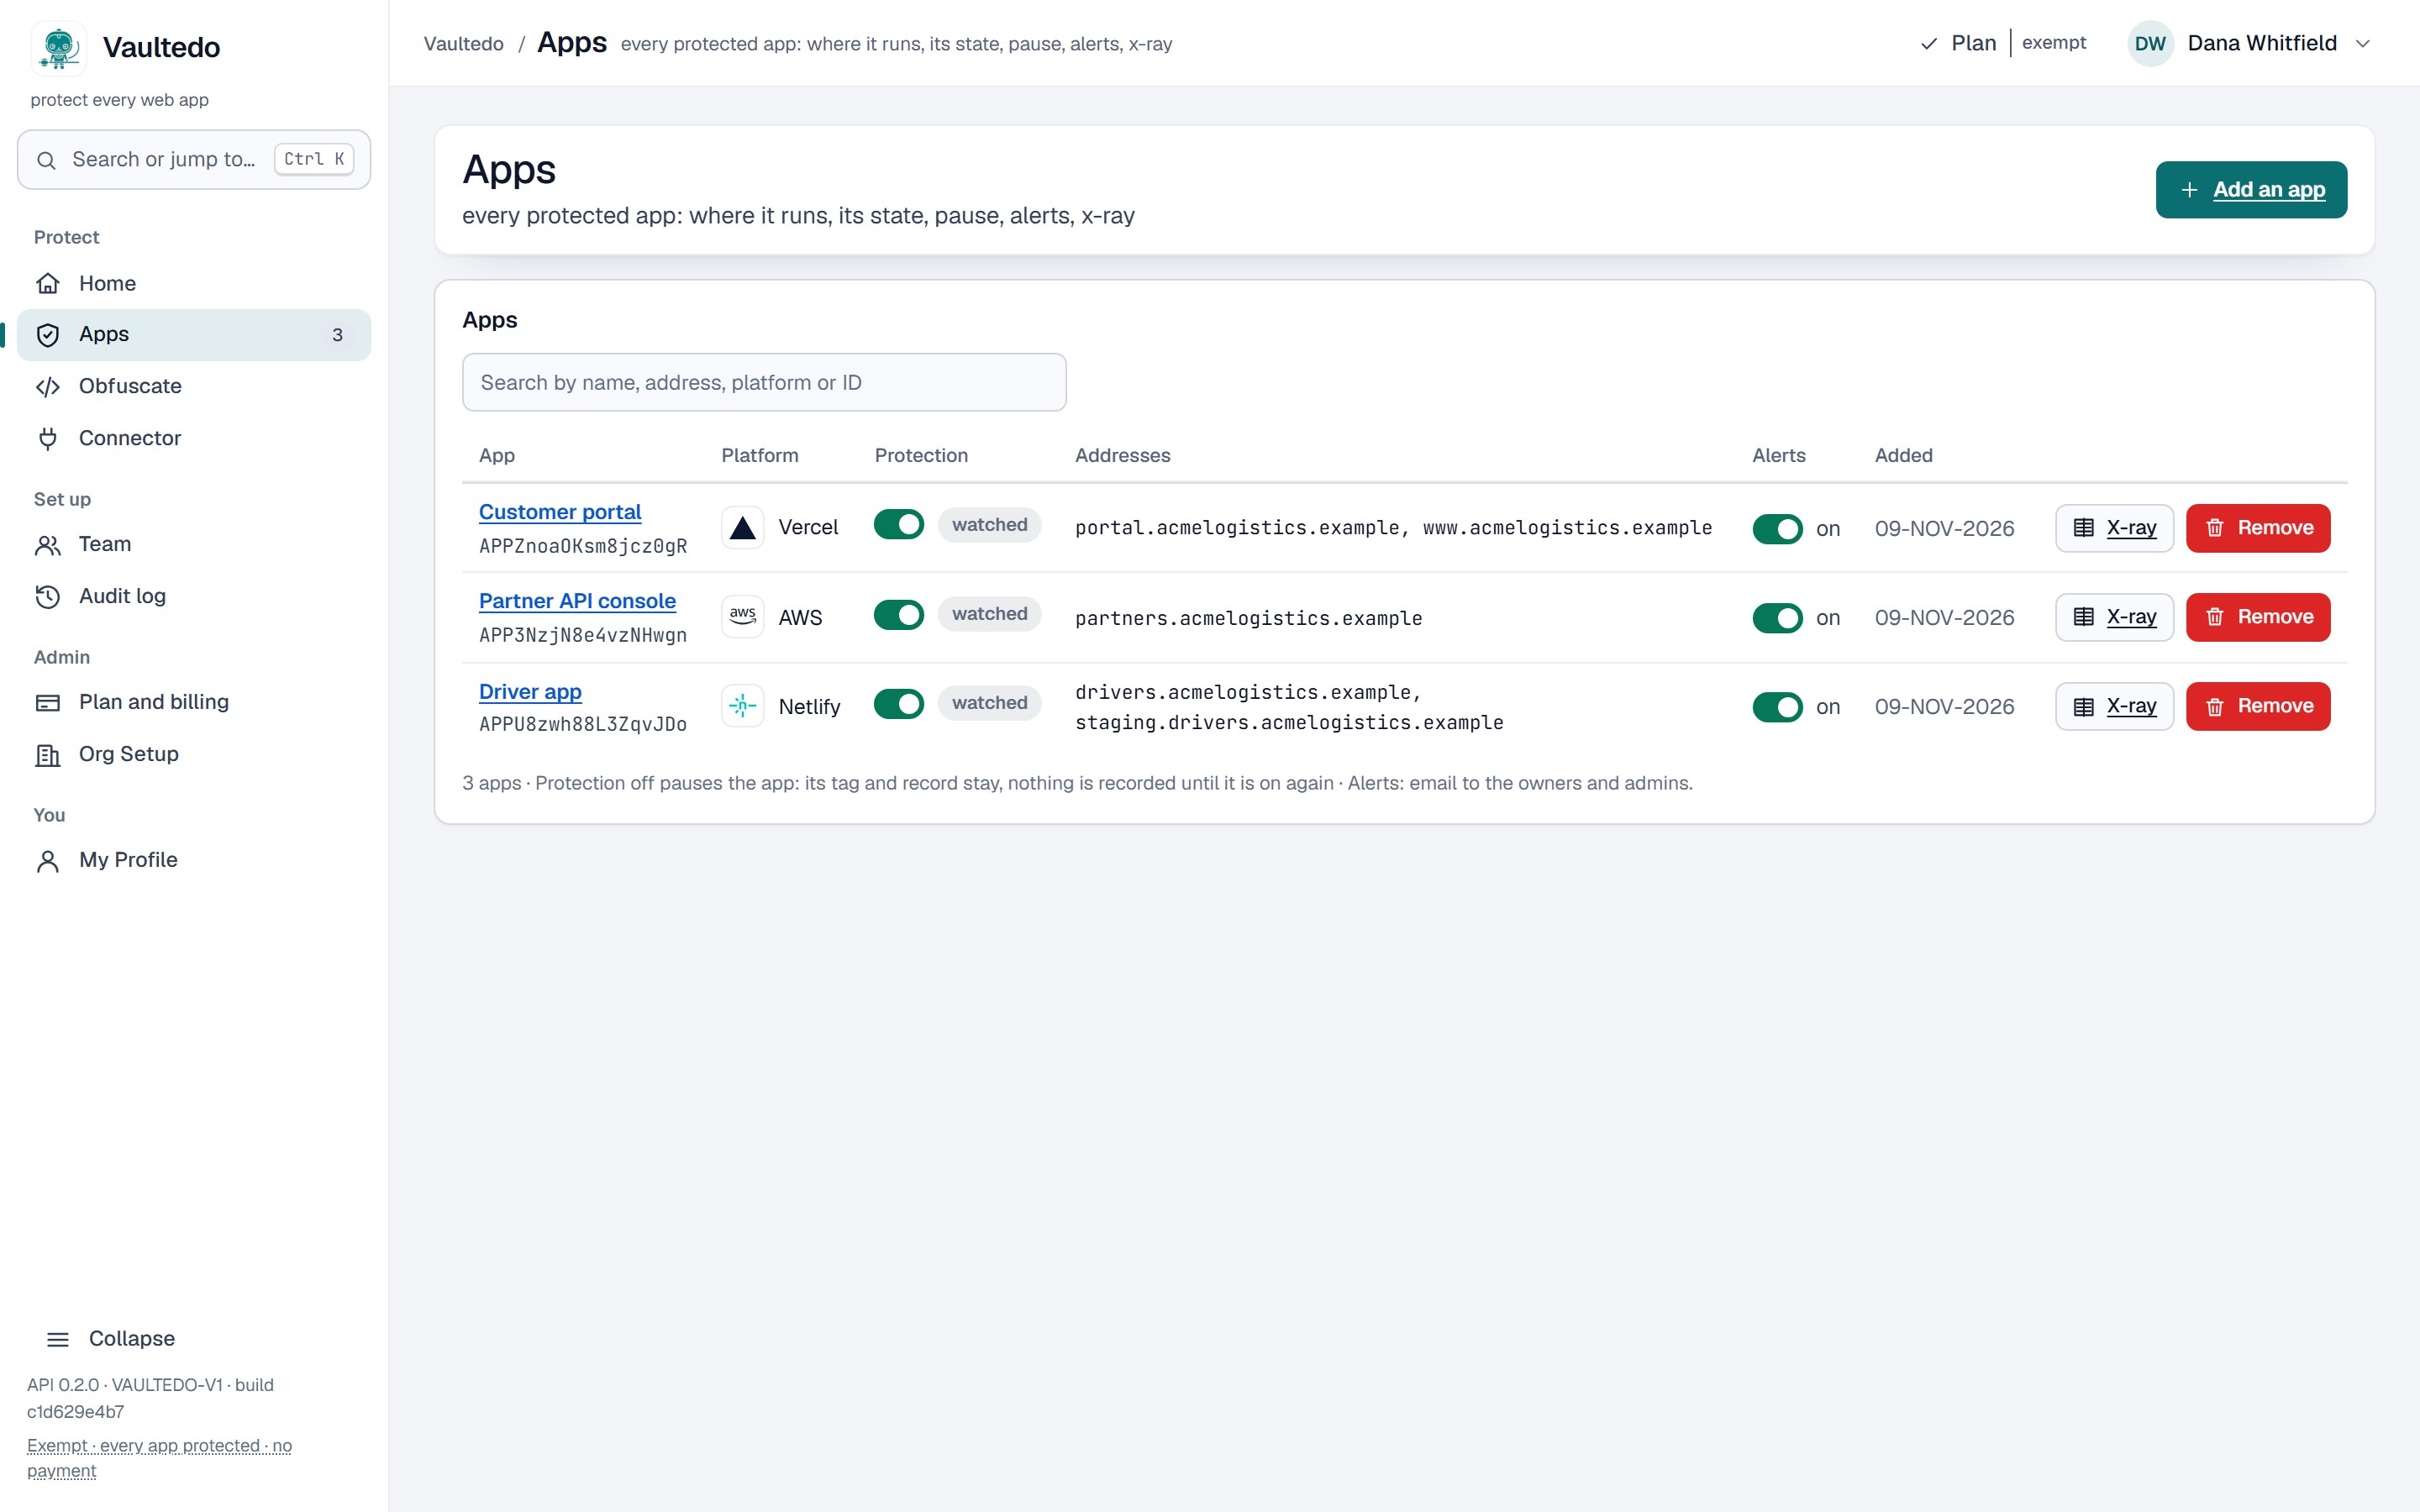
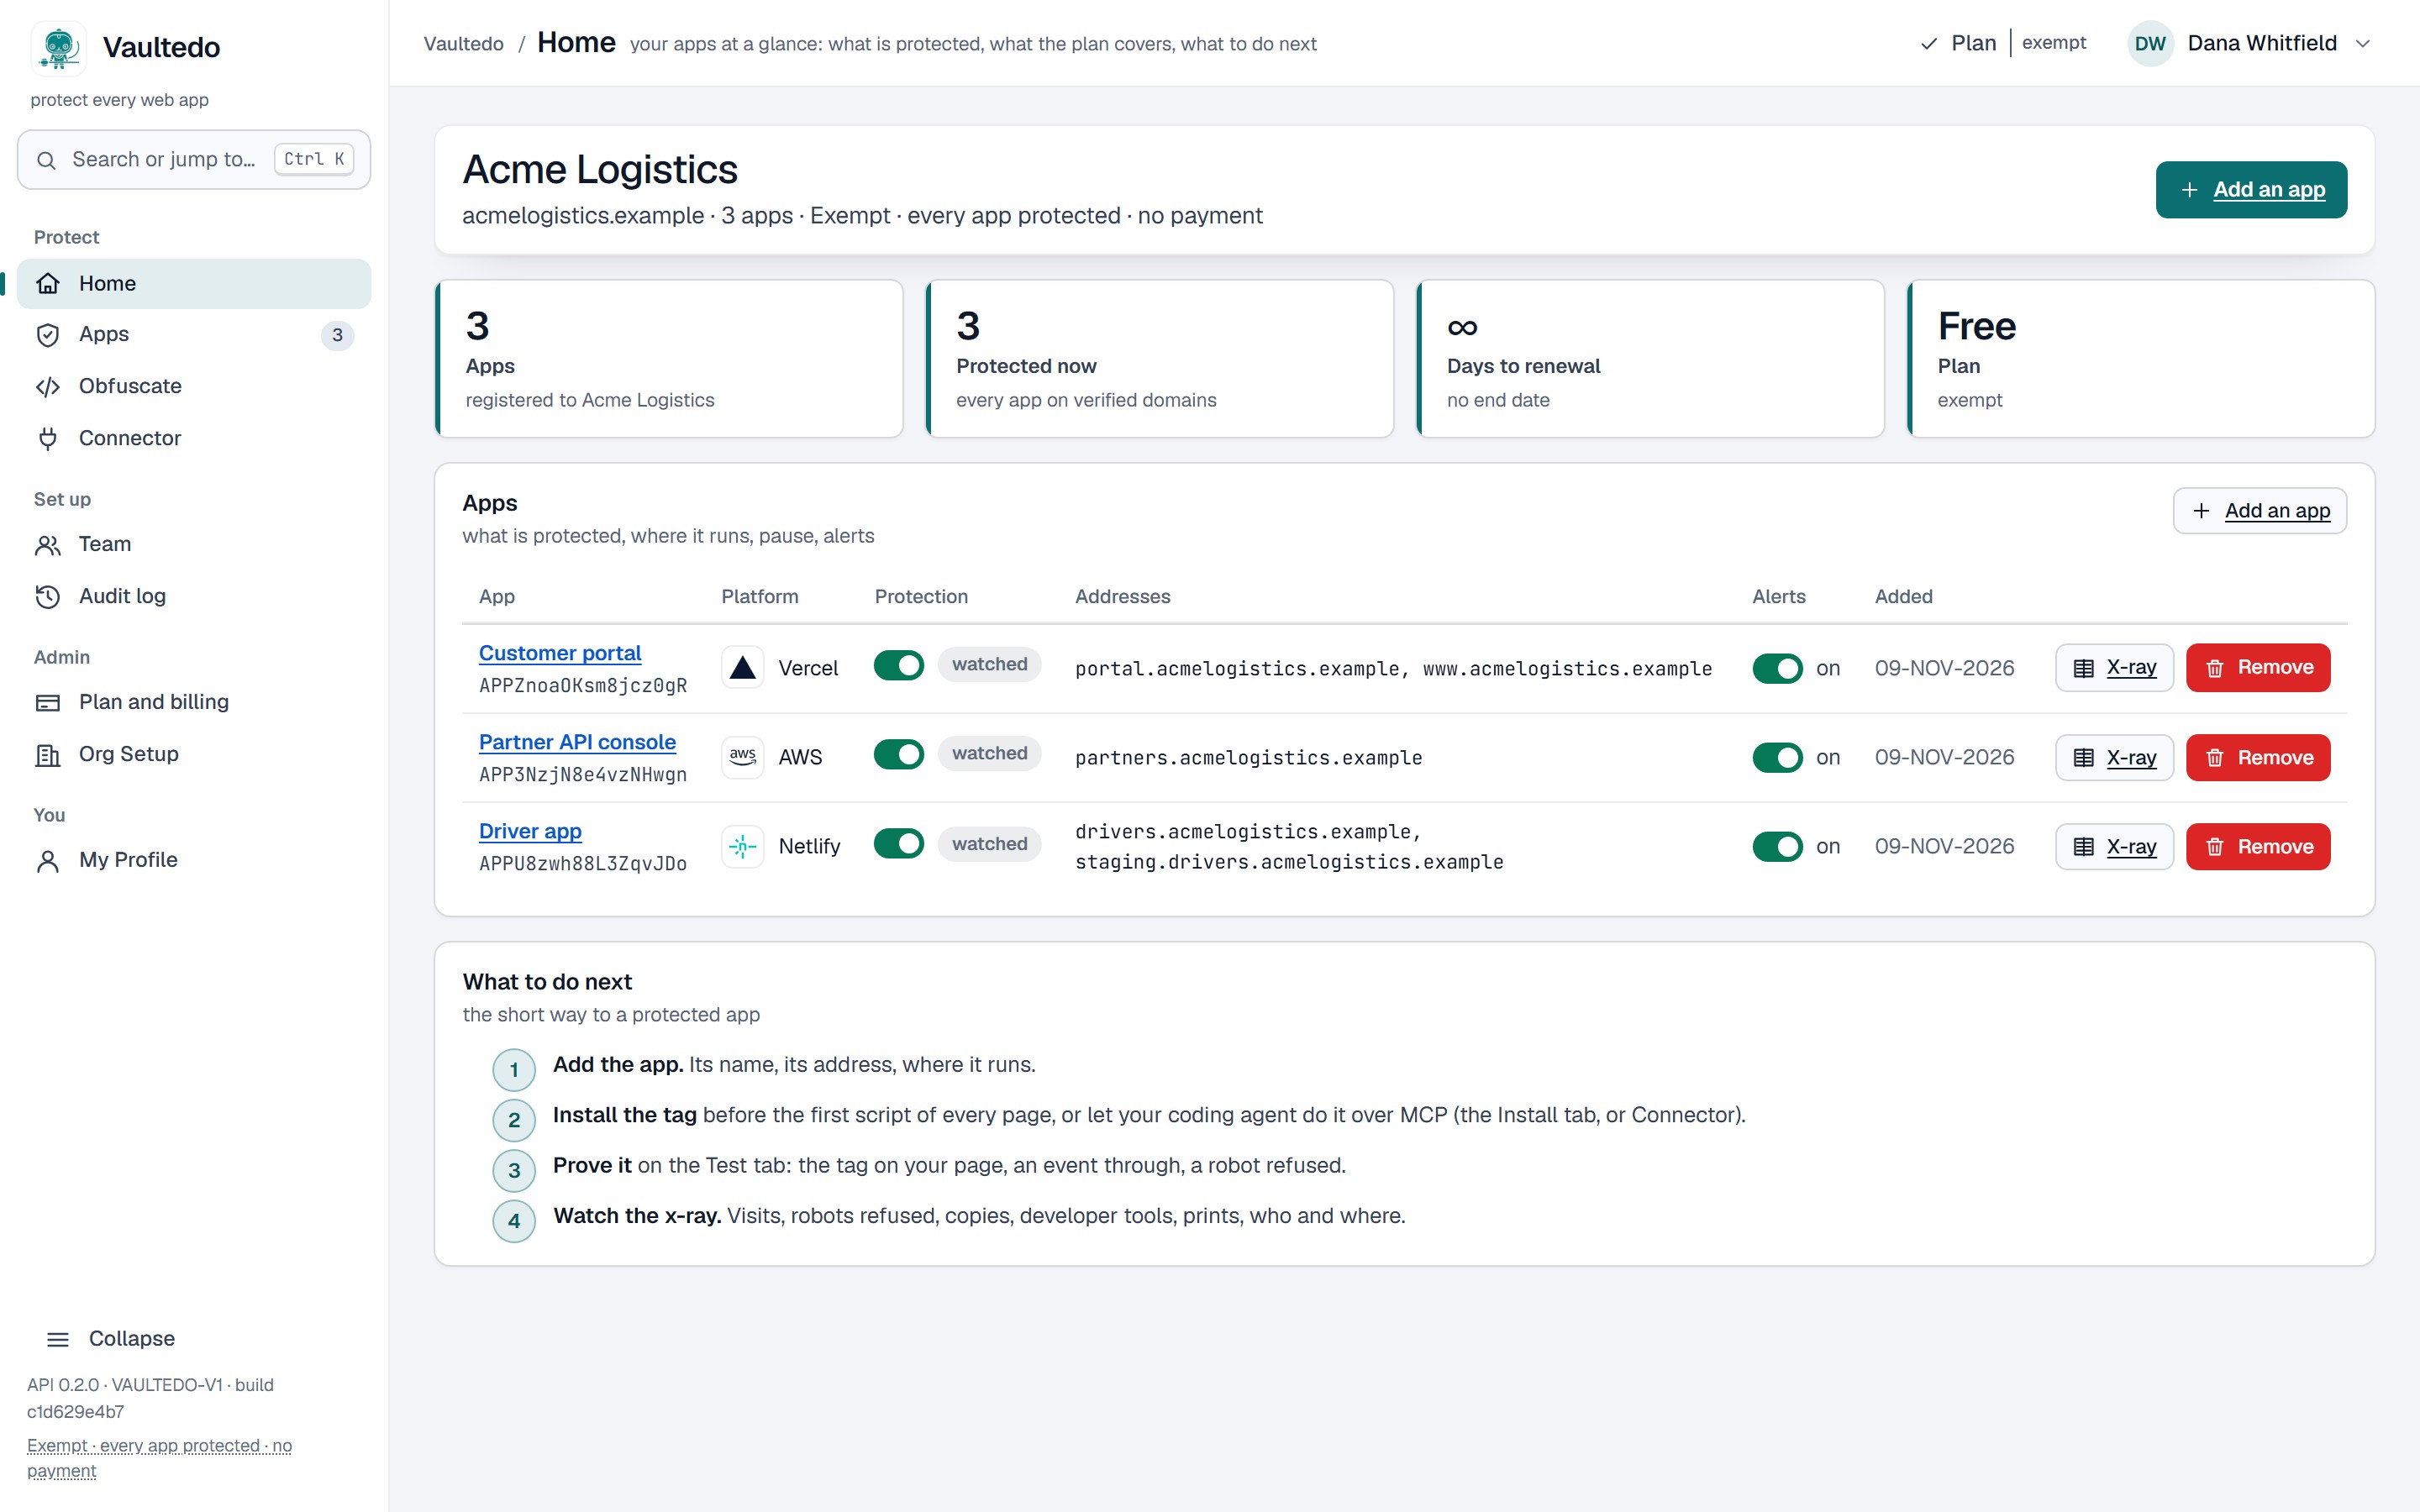
Each runs here with the real pieces of Vaultedo: the gate's answer, the shipped code and the mark.
A script requesting the customer list is refused. The same address from a real session is served as before.
function toast(title, kind, sub) {
  var t = document.createElement('div'); t.className = 'toast ' + (kind || '');
  t.innerHTML = '<b>' + esc(title) + '</b>' + (sub ? '<span class="sub">' + esc(sub) + '</span>' : '');
  $('toasts').appendChild(t);
  setTimeout(function () { t.style.opacity = '0'; t.style.transition = 'opacity .3s'; setTimeout(function () { t.remove(); }, 320); }, kind === 'err' ? 6500 : 3800);
}
document.getElementById("toasts"),window.t=function(t,e,s){var n=document.createElement("div");n.className="toast "+(e||""),n.innerHTML="<b>"+esc(t)+"</b>"+(s?'<span class="sub">'+esc(s)+"</span>":""),$("toasts").appendChild(n),setTimeout(function(){n.style.opacity="0",n.style.transition="opacity .3s",setTimeout(function(){n.remove()},320)},"err"===e?6500:3800)};A real function of this very console, before and after the build that ships it. Names, comments and structure are gone; the behaviour is not.
No web page can stop a screenshot. Every screen your application draws carries its viewer's invisible mark, so a leaked screenshot identifies its viewer.
Every protection product should state its limits.
Start free for 30 days: one app, watch mode, no card. The trial ends in a choice, never in an unexpected charge.
Payment through Paddle, card or invoice; a 14-day unconditional refund.
Every part of Vaultedo you install is one versioned file or image: checksummed, signed, installed from a link in your console, upgraded by us, and removed by one link.
A release is one file identified by its checksum, or one image identified by its digest. Nothing inside it can be edited by the subscriber.
Sign in, register your company, add the application and install one tag. The first attempt to copy it appears in your console with who and where.